We’ve added support for configuring server-level firewall rules in Frappe Cloud.
You can now define firewall rules directly from the server dashboard to control network access.
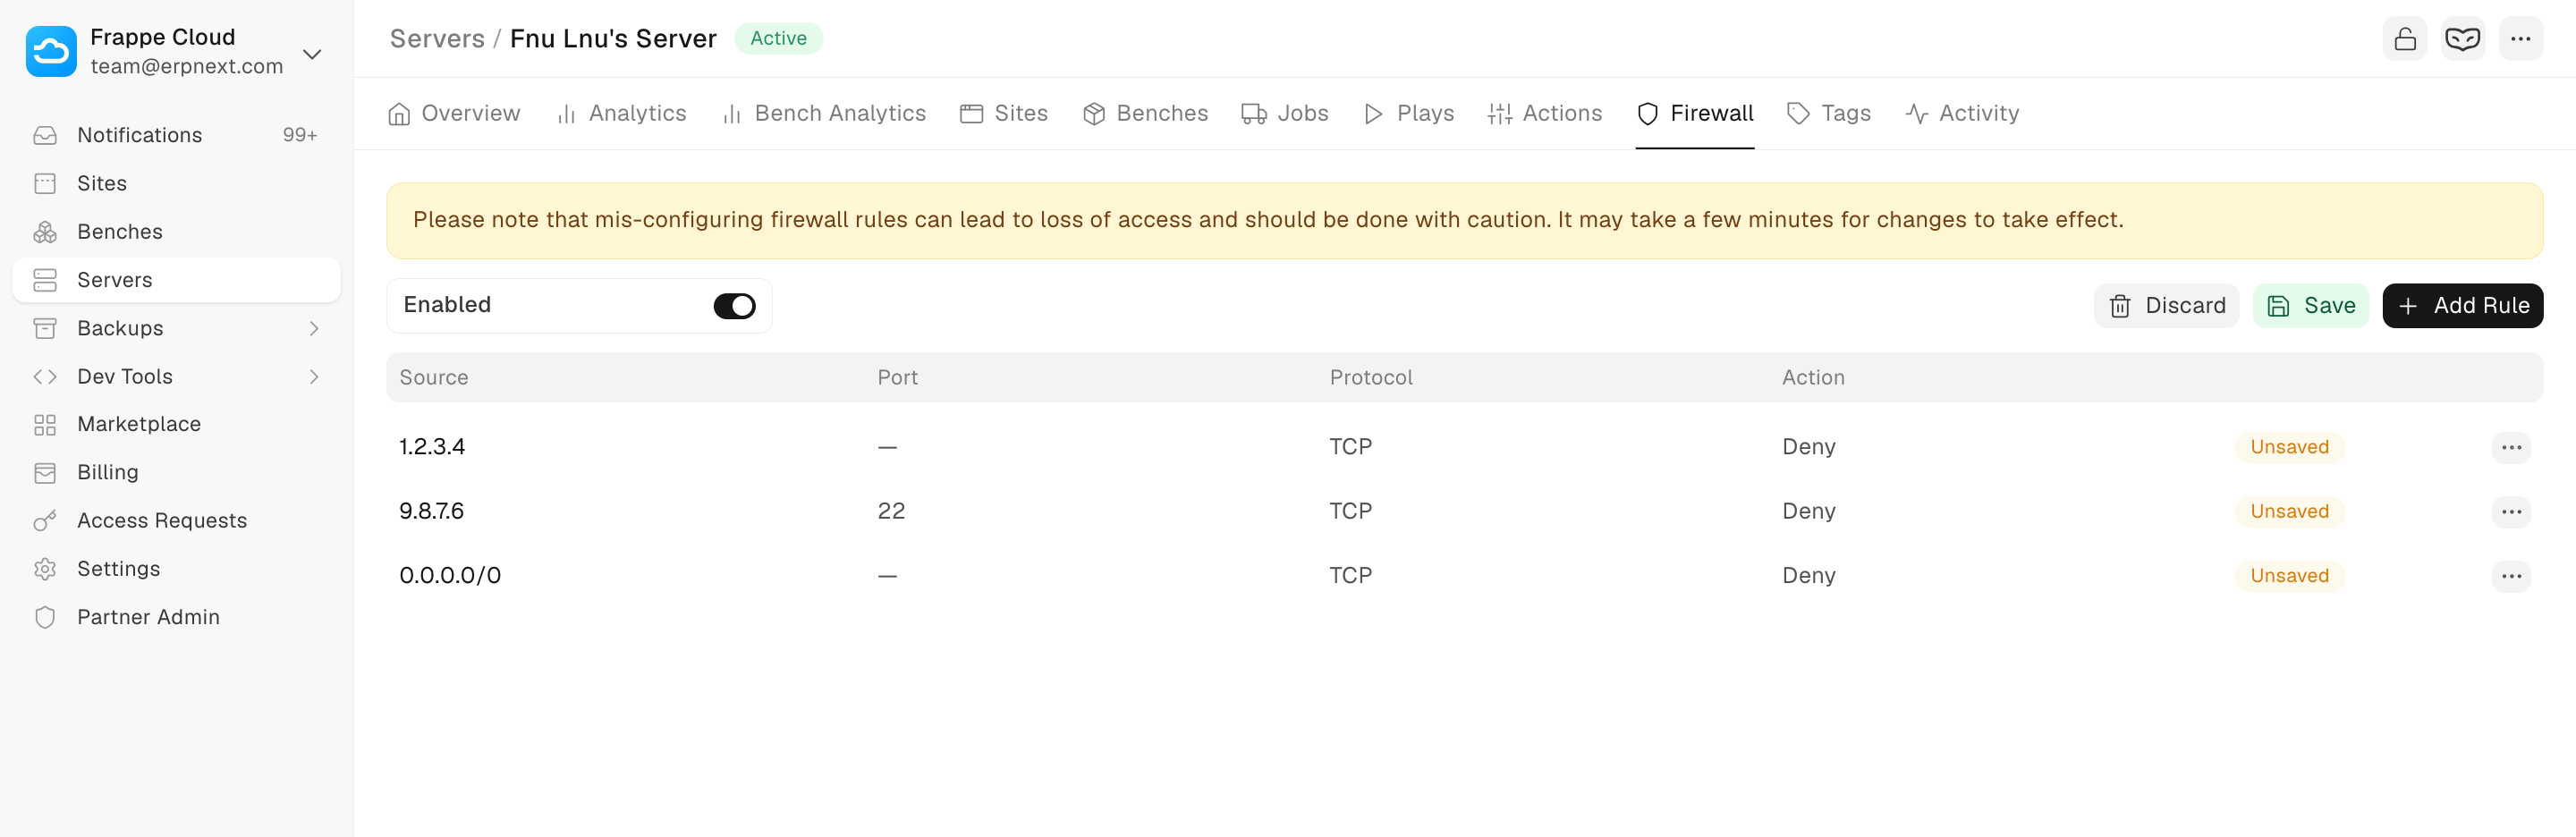
Supported capabilities include:
-
Allow or block specific IP addresses
-
Restrict access to specific ports (for example SSH)
-
Add deny rules to block unwanted traffic
This gives teams more control over network access and makes it easier to enforce security policies at the server level.
You can find the feature under: Server → Firewall
If you have any feedback or run into issues, please let us know.
