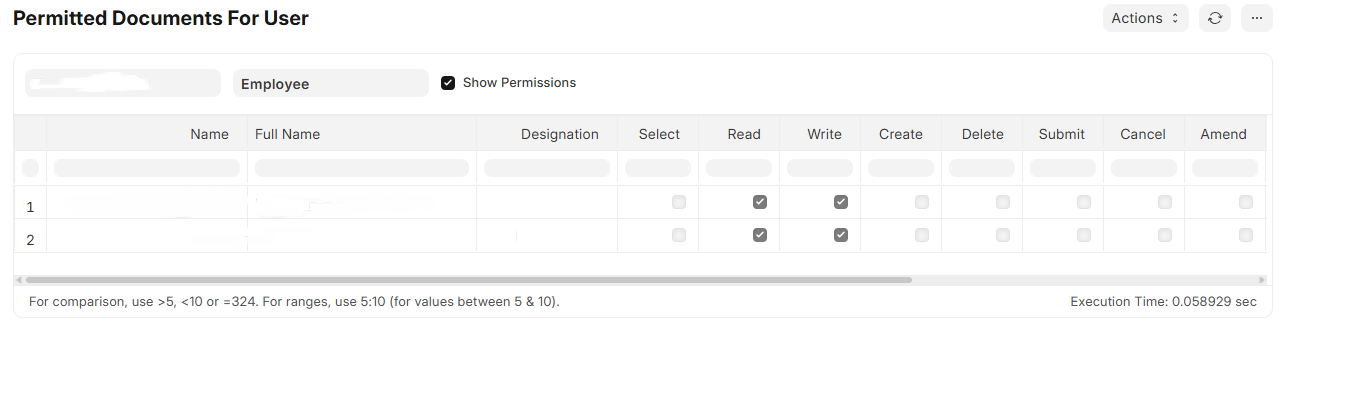
I’m encountering a permissions issue in ERPNext vXX (please replace with your version):
A user ([email protected]) has a User Permission set to view only one specific Employee record (say, Employee ID EMP001). However, this user is somehow able to view another Employee record (EMP002), which is:
- Not listed under their User Permissions
- Not linked to the user via the
user_idfield - Not explicitly shared with the user (
DocSharetable checked) - Not covered by any permissive role under Role Permission Manager (verified roles one by one)
Still, has_permission('Employee', 'EMP002', user='[email protected]') returns True.
I’ve tried clearing the cache, double-checked role-based permissions, and confirmed the record is not shared. Yet the user can access that unrelated employee’s profile.
Has anyone else faced this issue or is there another layer of implicit permission logic I may be missing?